0%
0%
INDUSTRY FOCUS
Your product velocity is excellent. The operational layer behind it, reconciliation, regulatory reporting, fraud monitoring, often isn't. Technology that doesn't fit FinTech workflows gets abandoned in 90 days
 OPERATIONAL VULNERABILITIES
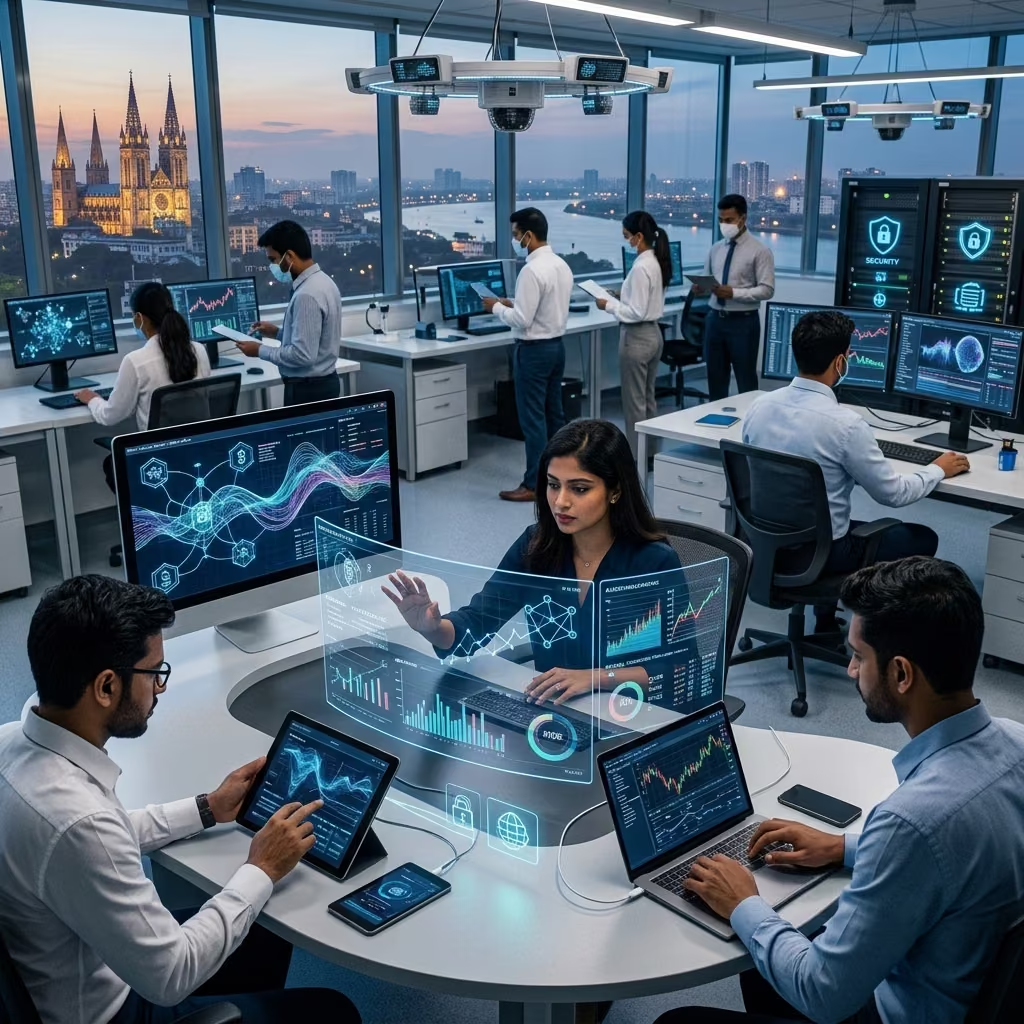
Financial workflows carry a higher cost of error because transactions, records, controls and reporting have to agree. Fragmented processes create reconciliation work and make exceptions harder to investigate.
Transaction, ledger, payment and operational records can require repeated comparison across systems. The more reconciliation depends on spreadsheets, the harder exceptions become to trace and resolve.
Fraud alerts, payment failures, documentation issues and unusual transactions can generate queues that require human review. Without structured routing, important exceptions compete with routine work.
Management and regulatory reporting can pull information from several operational systems. When data preparation remains manual, reporting teams spend valuable time assembling the picture instead of analysing it.
Customer, transaction, risk and operational information can be distributed across core platforms and supporting applications. Without a dependable data layer, teams argue over which number is correct before making a decision.
FINTECH SOLUTIONSBring customer, transaction, approval, reconciliation, reporting, and operational workflows together through structured digital processes.
Build role-based access, approval controls, audit trails, and workflow governance into the operational architecture.
Reduce repetitive financial operations by automating data movement, reconciliation workflows, reporting processes, and notifications.
Create clearer access to operational and financial information so decision-makers can identify exceptions, trends, and performance more effectively.
ENGINEERING PRINCIPLESFinancial technology requires security-first architecture, regulatory awareness, high availability, and precise data management.
Systems fail when developers treat compliance reporting as an export feature instead of a core architectural requirement.
A close process that's "mostly right" isn't right, financial systems are designed for exact accuracy, not approximation.
PCI-DSS-aligned handling, encryption, and audit logging are designed in from day one, not patched in before a compliance review.
 FAQ
Yes. We build on top of existing infrastructure where possible, assessed during the diagnostic before recommending any replacement.
Fraud monitoring thresholds are tuned against your actual transaction patterns during the build and testing phase, not deployed on generic defaults.
We'll flag that distinction. Automating low-risk verification frees up review capacity for the cases that actually need human judgment. It doesn't replace the need for reviewers on high-risk cases.
India-based cloud data residency is standard for financial services engagements, confirmed against your specific regulatory requirements during onboarding.
Inside our standard 90-day sprint structure, covering the diagnostic, build, and verified rollout.
READY TO BUILD?Tell us what you're building. We'll tell you how to ship it — fast.